Carziqo, a click-a-button Ponzi scheme, has collapsed. On October 12, 2026, all known website domains went offline. Investor withdrawals were also disabled. This pattern is typical of these short-lived schemes.
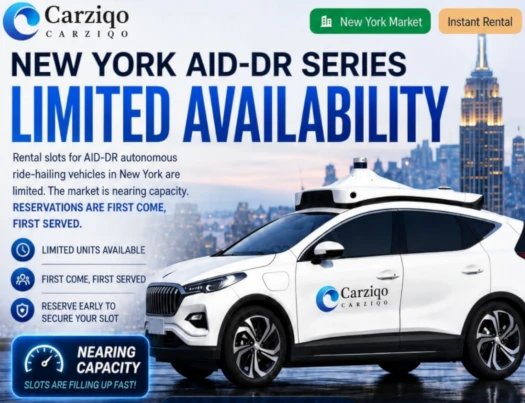
Carziqo presented itself as a vehicle leasing platform. It told investors they were funding rentable car fleets operating in various U.S. cities. In reality, no vehicles existed. The scheme simply used new investor money to pay earlier participants their promised returns. On top of the Ponzi structure sat an MLM pyramid that rewarded top recruiters.
Chinese operators ran the platform. Their main target market was the Philippines.
Instead of admitting the scheme had failed, the operators launched a familiar “hackers” narrative. The first emergency notice appeared about seventeen hours before the full shutdown.
The message claimed a hacker group had attacked the servers. It said the attackers changed users’ bank card details and stole funds. The company promised to compensate a “small number” of victims through senior managers. At the same time, it cancelled all withdrawals “to protect remaining funds.” It also claimed car products and daily income were still running normally.
About an hour later, a second notice appeared. It described the downtime as a routine “system optimization upgrade” expected to finish in five hours.
Roughly thirty minutes after that, Carziqo issued its last official update. The company repeated the hacker story. It claimed it had already compensated stolen accounts. It then declared every user a “risk user.” All account funds and robot products were locked.
Users were told they must log in and complete a verification process to unlock their accounts. Anyone who failed to verify within a set time would be labeled a hacker. Their funds would be confiscated and their details handed to authorities.
Every one of these statements was false. The real goal was to extract more money from remaining investors. Those who log in to “unlock” their accounts will almost certainly be asked to pay a fee. Paying that fee will not restore withdrawals. It will only increase losses.
Because many Philippine residents invested in Carziqo, copycat schemes started almost immediately. One reboot is already live on the domain crziqo.digital. That domain was registered on the same day the original platforms went dark. It is simply another attempt to collect more money from the same group of victims. It will collapse the same way.
Investors who lost money in Carziqo have almost no chance of getting it back. The operators are Chinese scammers based in jurisdictions where law enforcement is often compromised. Funds have already been moved beyond reach.
Anyone offering “Carziqo recovery” services or recruiting into similar click-a-button apps is running a secondary scam. These recovery pitches and reboot platforms are designed to take whatever money victims still have left.
Carziqo’s collapse follows the exact pattern seen in every click-a-button Ponzi tracked since 2021. The outcome was never in doubt.
There are no reviews yet. Be the first one to write one.